If the assistant can see it, someone can ask for it. Filtering the answer afterwards is not a control.
On the last blog we talk about retrieval that can’t find the one document that matters. Today is the opposite failure, and it’s the one that ends deals: retrieval that finds a document it never should have.
Here’s how most enterprise assistants get built. A team connects the model to the document store, the warehouse and the CRM with a service account that can read everything. Then they add a line to the system prompt: only answer using information the user is allowed to see.
That’s not access control. That’s a request. And it’s being made to the one component in the stack that’s designed to be persuadable.
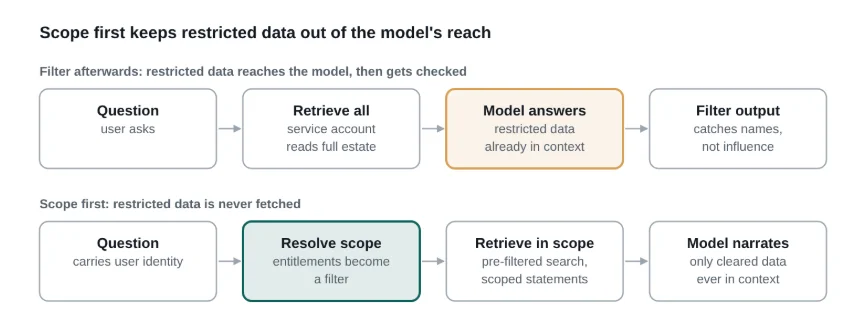
The filter-after design has a simple order of operations. Retrieve broadly, generate an answer, then check the answer for anything the user shouldn’t see. Three things go wrong with it, every time.
None of these are model bugs. They’re architecture. If a component can read something, you are relying on its judgement not to use it, and judgement isn’t a control a risk committee will sign.
“Permissions” hides two separate questions, and most assistants only answer the first.
Role-based feature access is the easy half, and it’s what most security questionnaires get answered with. Data entitlement is the half that matters. An analyst with exactly the right role can still be shown the wrong client’s exposure if the retrieval layer reads the whole estate.
The rule we work to is short: the assistant should never be cleverer than the person asking. It can read, reason over and answer from exactly what that person could already open themselves, and nothing else.
In Equative Insights OS, entitlement is applied where the data is read, not where the answer is written. Every question carries the identity of the person asking from the first stage to the last.
Same four stages, different order of trust: in the first design the model is the control; in the second it never needs to be.
And it’s visible. The retrieval stage of every trace states the entitlement scope that applied, so a reviewer can see what the answer was allowed to draw on, not just what it did.
Most AI security reviews test refusals. Someone types a question they shouldn’t be able to answer, the assistant declines, and the box gets ticked.
That test proves the least. A refusal only shows the model chose not to say something it already had. The question that matters is the one underneath: could it have retrieved that at all?
If the honest answer to the first two is “service account” and “after”, the rest doesn’t matter much.
Permissions added late always end up as a filter, because by then the retrieval layer already reads everything and nobody wants to rebuild it. Permissions designed in early end up as a boundary, and a boundary is something security can actually test.